

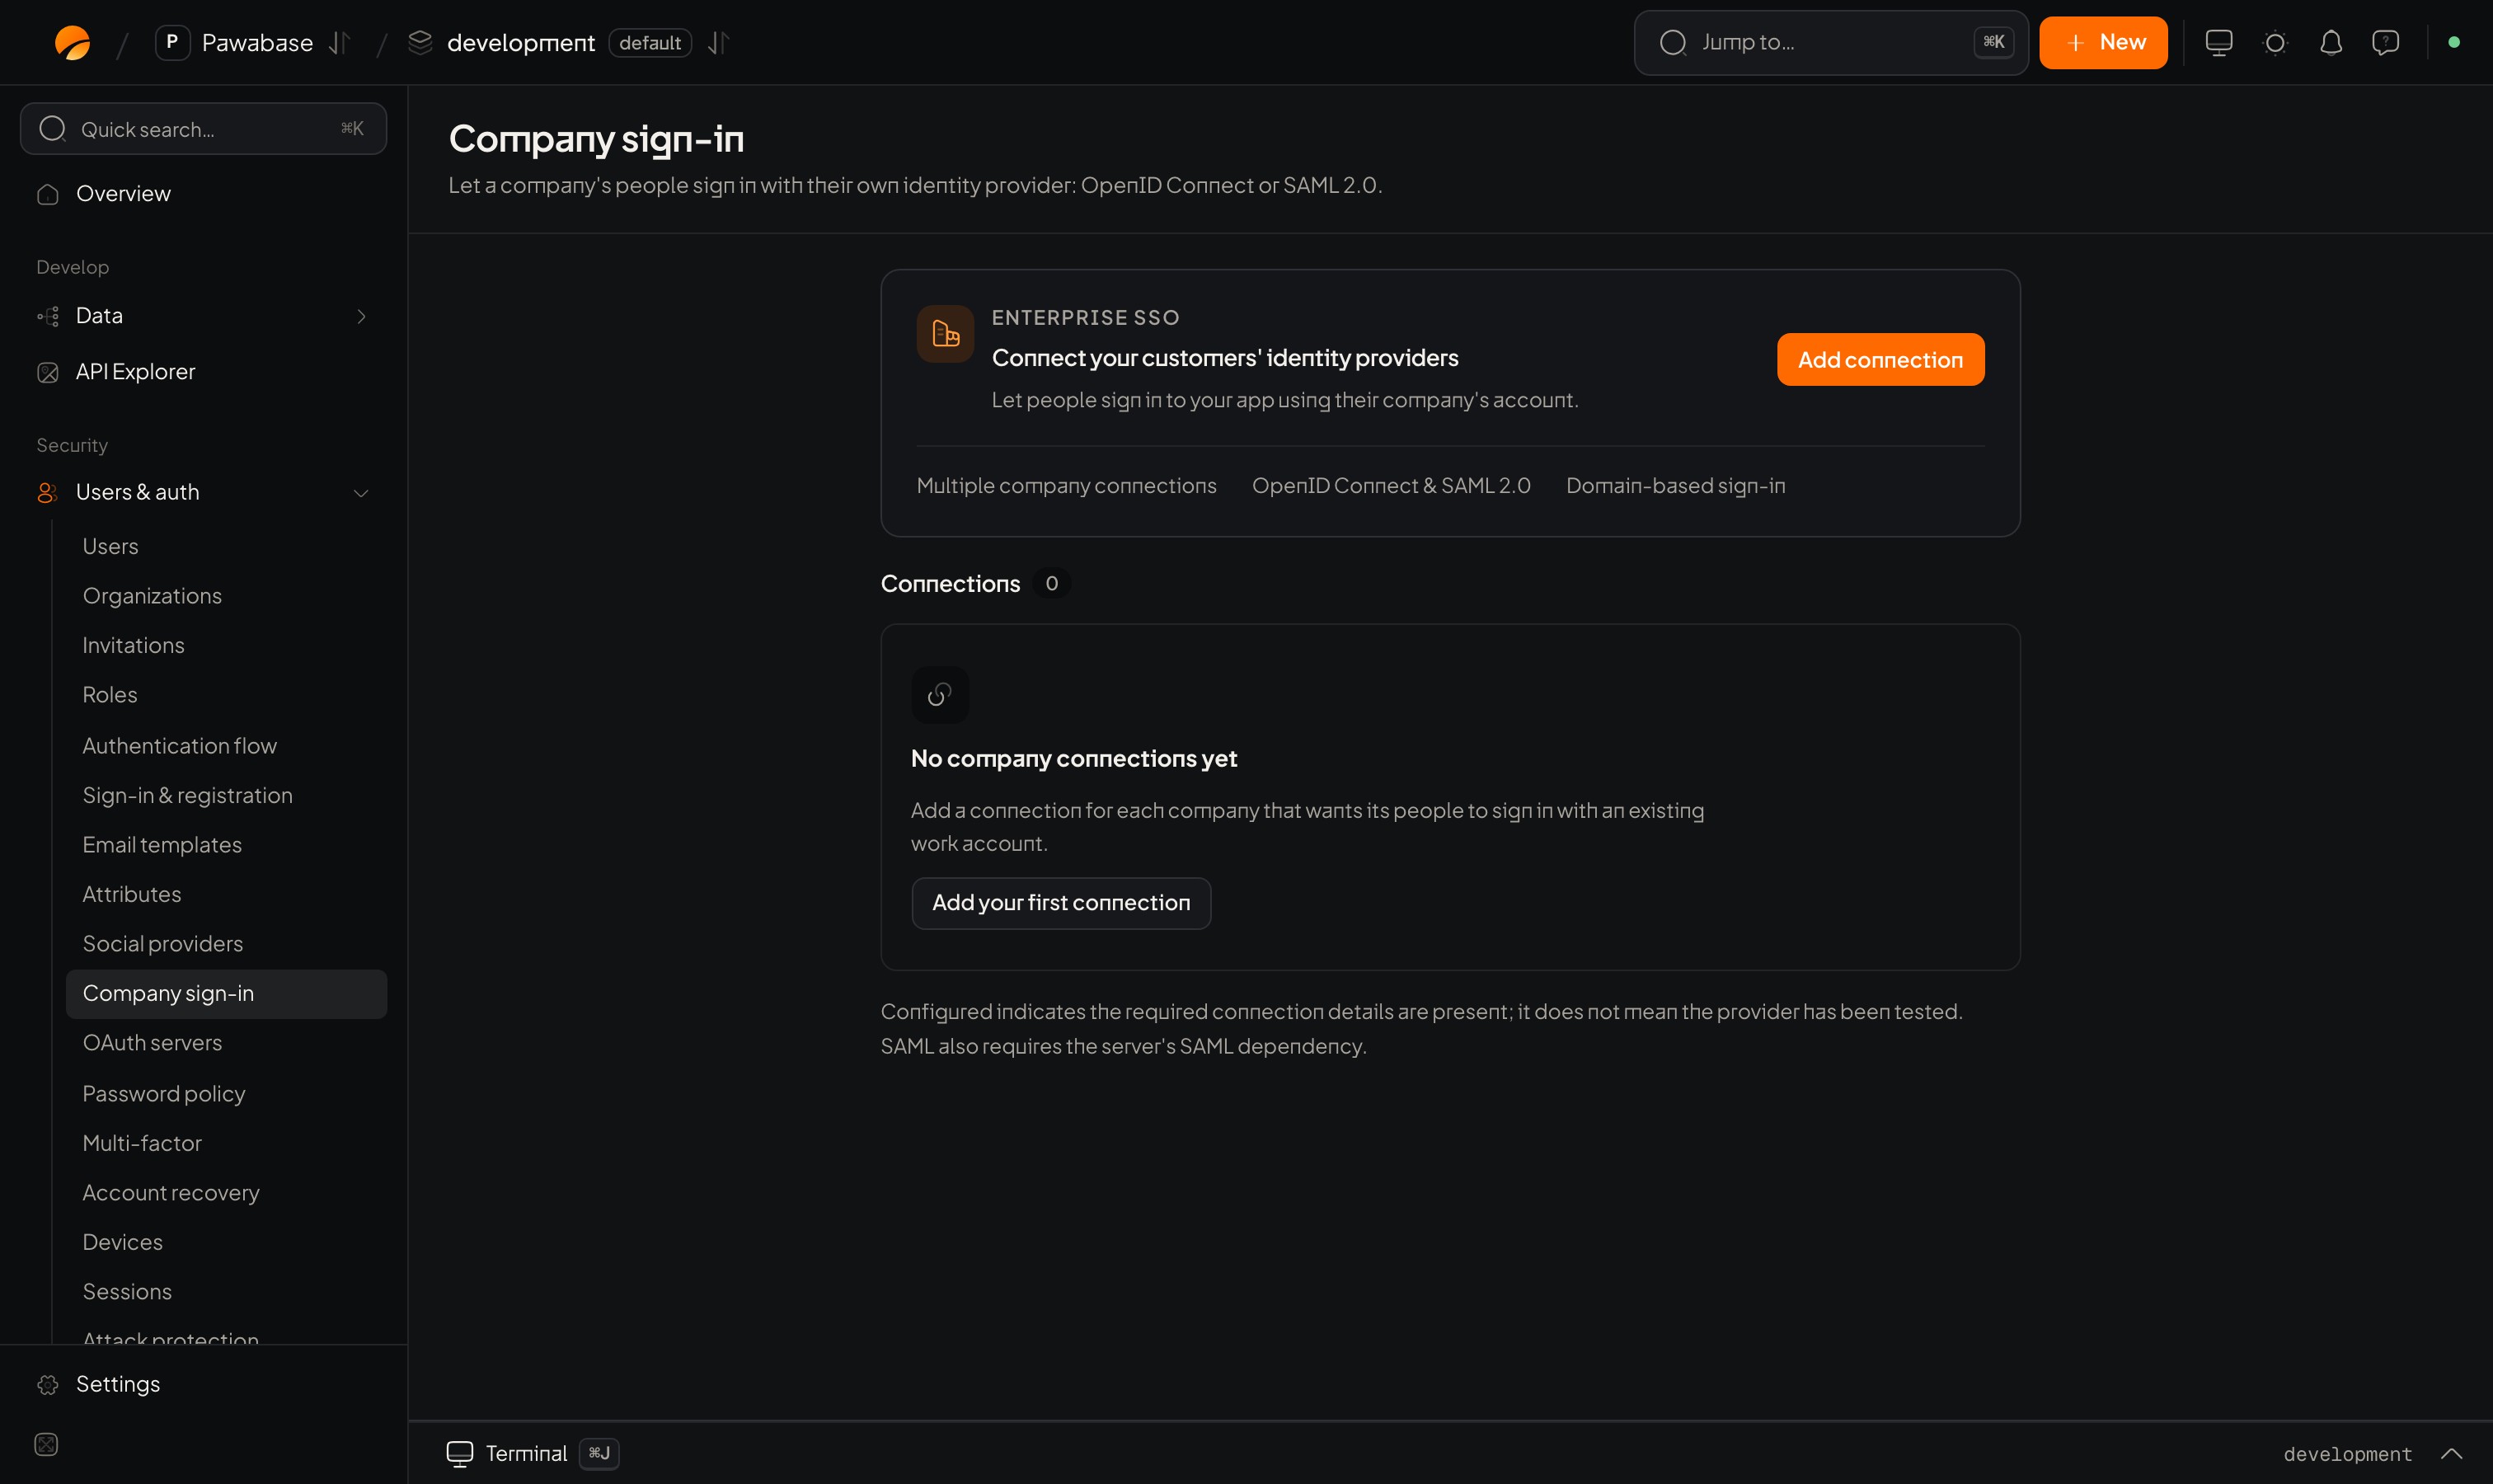
Users & auth → Company sign-in: Add connection.
In Studio
Users & auth → Sign-in → Company sign-in. The empty page says Connect your customers’ identity providers. Choose Add a company connection.1
How does the company sign in?
Choose SAML or OpenID Connect. Ask your customer’s IT team which they use; most support both.
2
Connection details
Fill in the fields below.
3
Finish setup with the provider
The page shows the values your customer must enter on their side. Send them across and ask the customer to test.
Connection details (both types)
SAML
Attribute mapping says which SAML attribute fills which Pawabase field: a table of Pawabase field (
name, email…) and SAML attribute (displayName…).
Give your customer these values to enter in their provider (shown on the Finish setup step): Entity ID, Assertion consumer service URL and Metadata URL.
OpenID Connect
Give your customer the Redirect URI shown on the finish step to register with their provider.
What people experience
- Someone types their work email on your sign-in page.
- Pawabase matches the domain to a connection and sends them to their company login.
- They sign in there (with their company’s own rules, including two-step).
- They return to your app, signed in. The first time, an account is created; the identity appears under their linked accounts.
Customer onboarding checklist
- Agree the protocol (SAML or OIDC) and the email domains.
- Create the connection; keep the secret in Secrets.
- Send the customer your Entity ID / ACS URL (SAML) or Redirect URI (OIDC).
- Receive their entity ID, SSO URL and certificate (SAML), or issuer, client ID and secret (OIDC).
- Enter them, tick Enable this connection, and have the customer test with a real user.
- Optionally turn off sign-ups for that customer’s domain so only company sign-in works.
Good to know
- Domain matching decides which connection applies, so use each company’s exact domains.
- Trust the email address matters if your rules need verified emails; only tick it for providers you trust to verify addresses.
- Certificates expire. Note the date and rotate it with the customer before then.
- Two-step verification for these users is usually enforced by the company’s provider; you can still require your own.
Organizations
Put the company’s people in one organization.
Secrets
Store client secrets.