

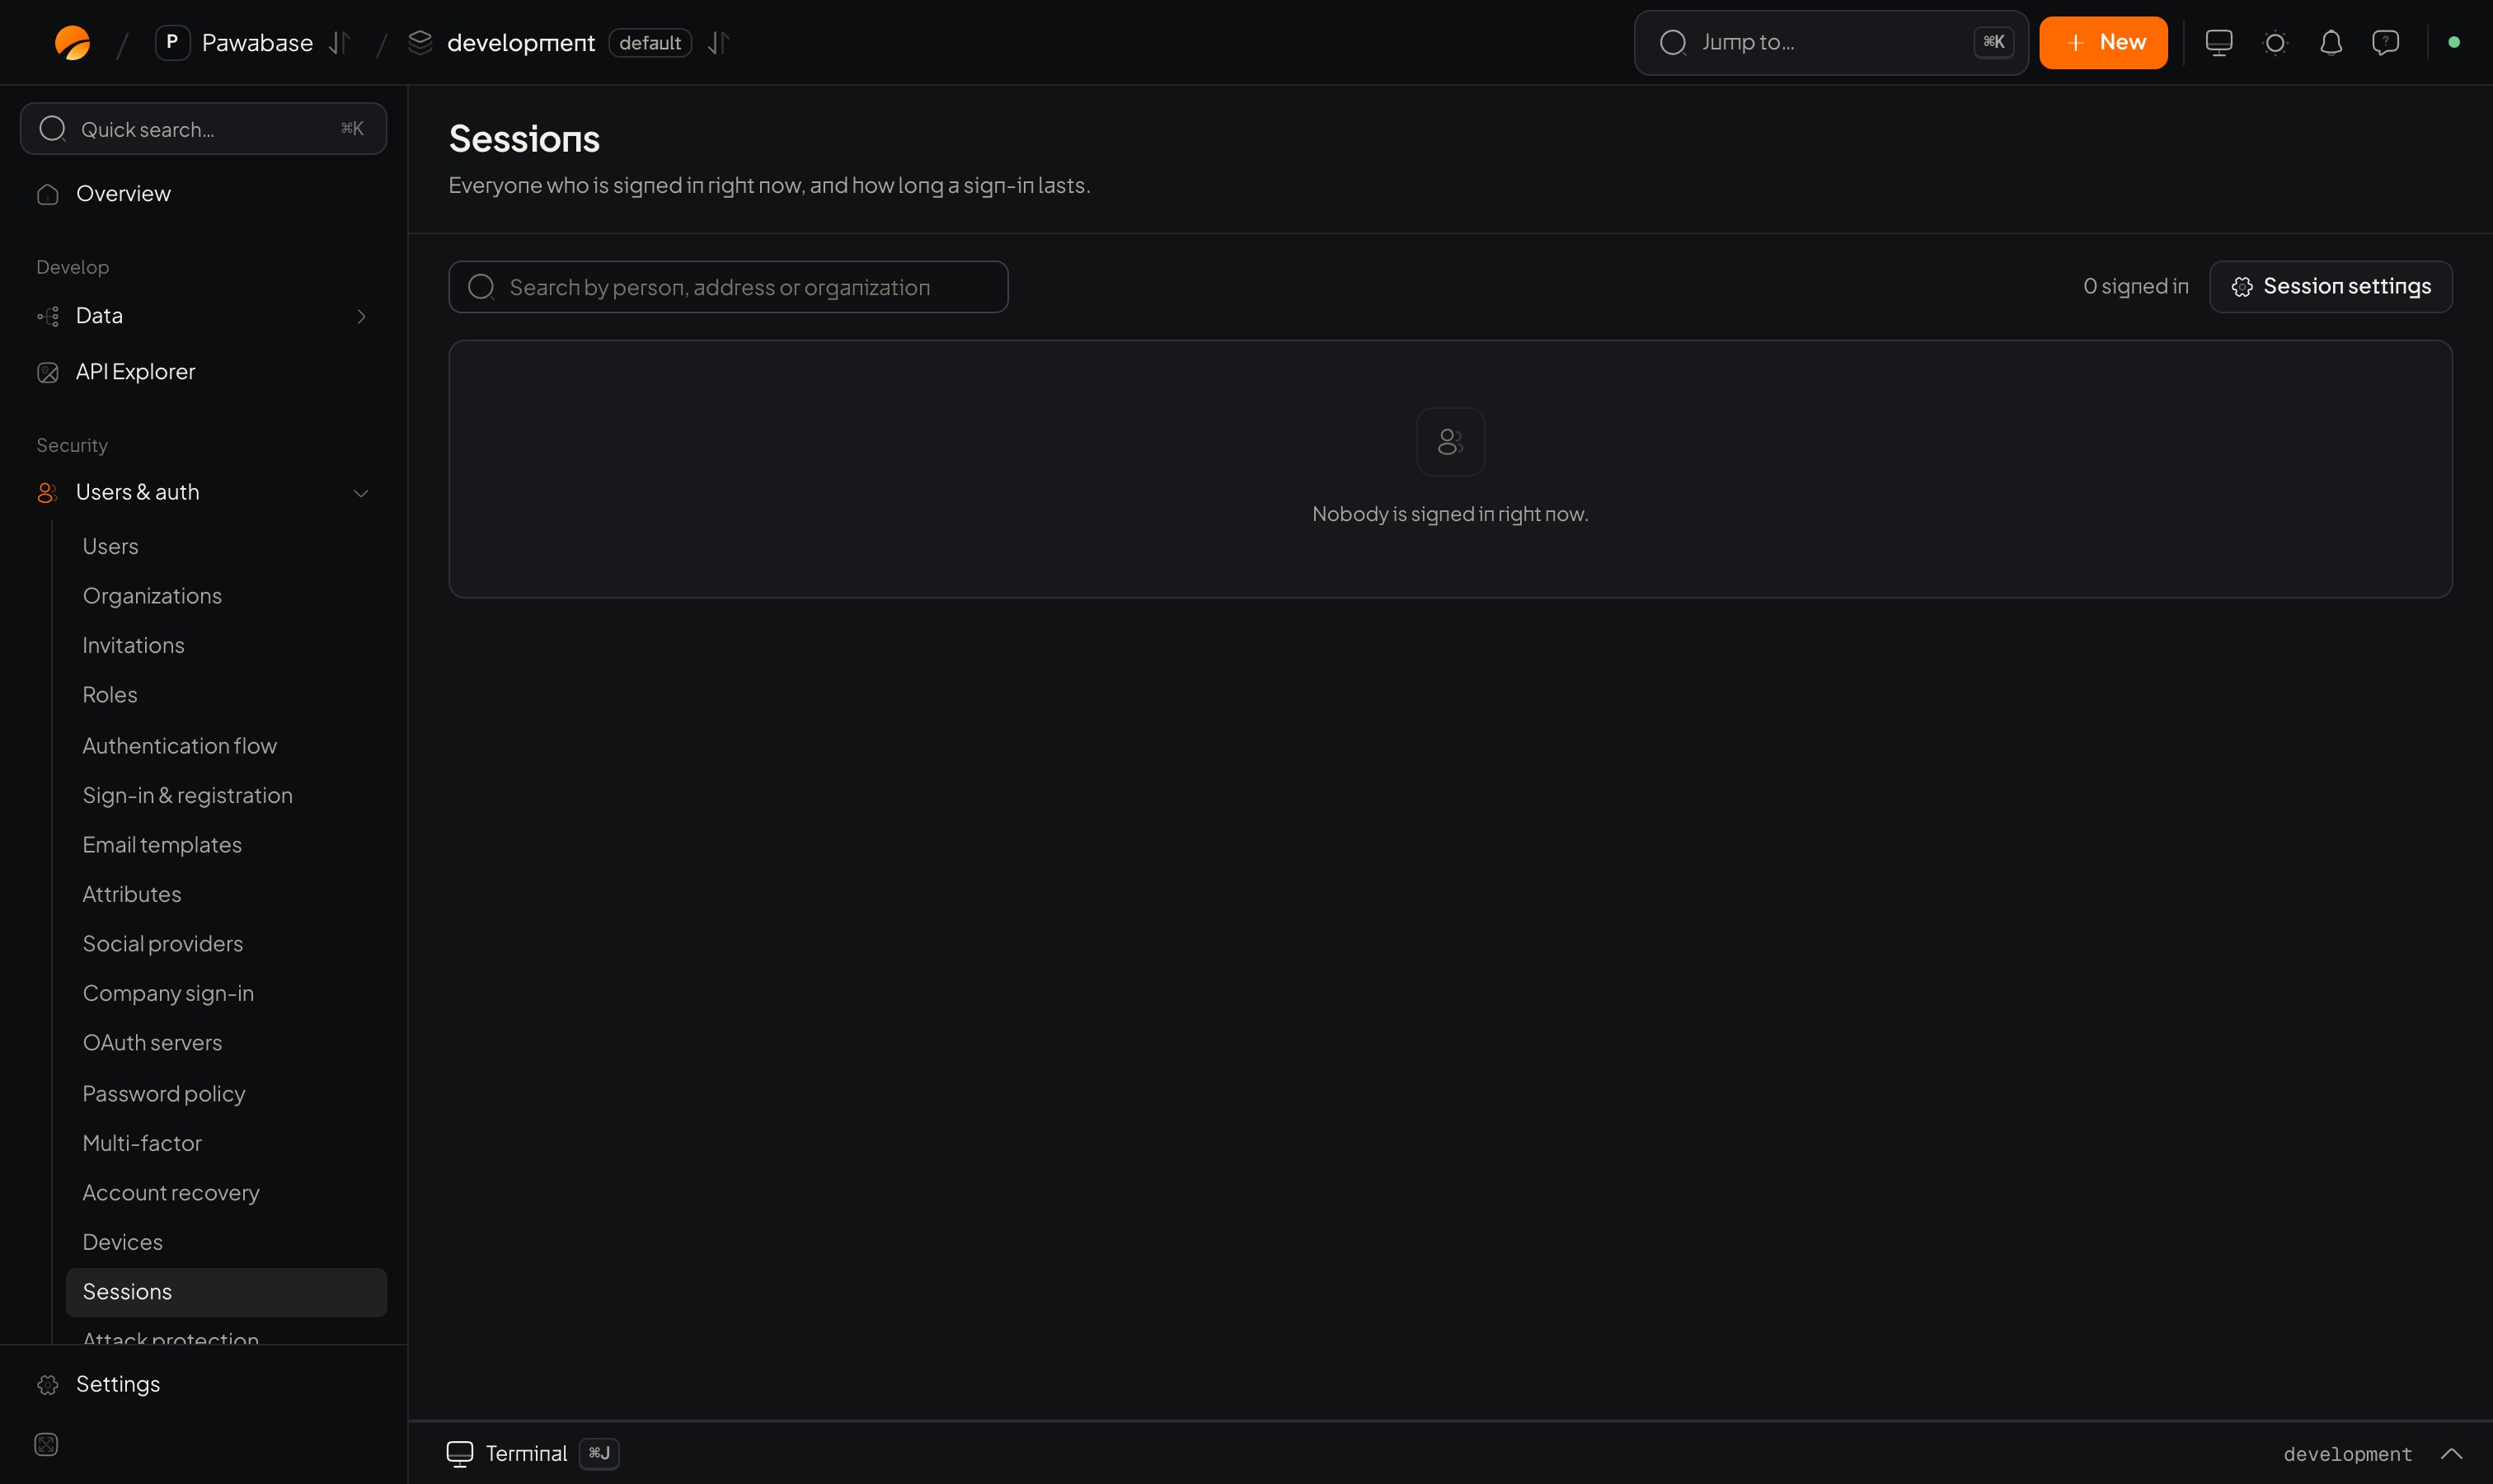
Users & auth → Sessions: active sessions, with Session settings.
In Studio
Users & auth → Security → Sessions. Access tokens are short and refresh quietly. A refresh token that is used twice ends the whole session, on the assumption it was stolen.Session settings
Active sessions
A table of live sessions (person, method, device, last active). From there an administrator can end a session.Choosing lifetimes
- Access token: keep it short. A shorter lifetime means a change (new role, disabled account) takes effect sooner, but costs a few more refreshes. 15 minutes is a good default.
- Refresh token: this is “how long until I must sign in again.” 30 days suits consumer apps; banking apps use hours. It resets whenever the person is active.
- Sessions per user: set a limit for paid seats or sensitive tools, so one account can’t be shared by a whole team.
Read the session in your app
access_token, refresh_token, expires_at, session_id, the active org and org_role, and the user.
React to changes
Subscribe once, near the top of your app:Sign out
SIGNED_OUT event fires.
Show “where you’re signed in”
current marks the session making the request; don’t offer to revoke that one, use sign-out instead.
Revoke from the admin side
To end sessions yourself in Studio: Users & auth → Security → Sessions lists live sessions, and a person’s own page (Users → the person → Security) can end them. To sign a person out everywhere, open them and use Sessions.Where the session is stored
Change it in the client options. React Native passes AsyncStorage; a cookie-based framework passes its own object with
getItem, setItem and removeItem:
persistSession: false for a script that should remember nothing. In Python: Pawabase(url, key, session_store=FileSessionStore("~/.myapp/session.json")).
Two tabs refreshing at the same moment would end the session, because refresh tokens are single-use. The client prevents this by sharing one refresh across calls and, in browsers, across tabs. You don’t need to do anything.
Events
session.revoked fires when a session ends (signed out, expired or revoked), and session.reuse_detected when a stolen refresh token was replayed and the family was revoked. See Auth webhooks.
Devices
Track and remember devices.
Auth in React
Use sessions in components.